Showing posts with label Bill Cobb. Show all posts

Sunday, May 20, 2007

eBay Members Crying Out for Better Security


It has been more than a month since Rob Chesnut, eBay's Senior Vice President of Global Trust & Safety, announced to the eBay community that new fraud prevention initiatives were implemented on eBay's platforms. However, this blog has mentioned many times since Chesnut made his announcement that we have not seen any signs of the new initiatives. Nothing proactive has occurred, eBay member accounts are still being hijacked and fraudulent listings continue to appear on eBay's platforms 24/7/365.

However, there is a simple solution to instill member confidence in eBay, and that is for eBay to require all of its members to use the PayPal key fob that was rolled out onto PayPal's platform in March. Called the "PayPal Security Key", PayPal gives it free of charge to all users that have business accounts and charges $5 to users that have premiere or personal accounts. The "PayPal Security Key" can also be used on eBay, and eBay gave the "PayPal Security Key" to eBay PowerSellers at a certain level for free.
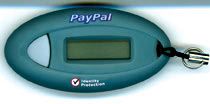
Although the "PayPal Security Key" does not stop fraud, by using it, members have some comfort knowing that they have added an additional layer of security to both their PayPal and eBay accounts. PayPal spokesperson Sara Bettencourt told CNET News.com in January that "If a fraudulent party somehow got hold of a person's username and password, they still wouldn't be able to get into the account because they don't have the six-digit code."

Just as eBay does not want to require new members to take tutorials to learn how to protect themselves from fraud, eBay does not want to require all of its members to use the "PayPal Security Key". However, we have a few solutions to at least instill buyer and seller confidence on eBay's platforms, and an additional enhancement for PayPal to implement. Moreso, the solutions are simple because PayPal and eBay have already rolled out and implemented the "PayPal Security Key".

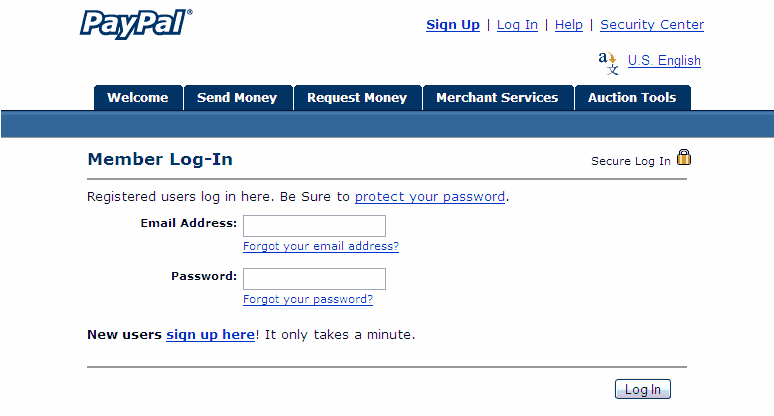
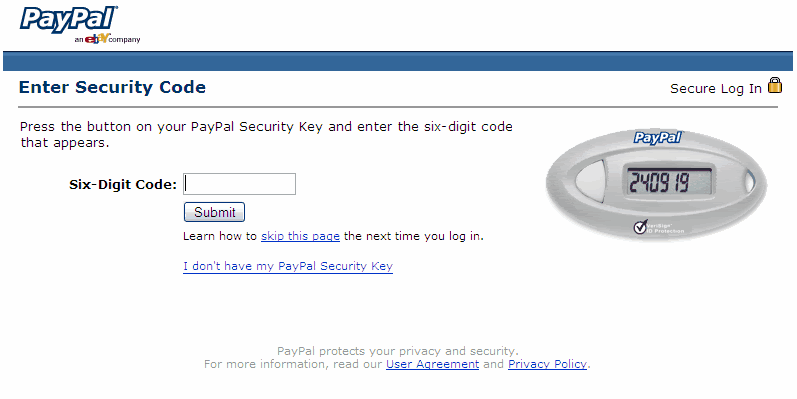
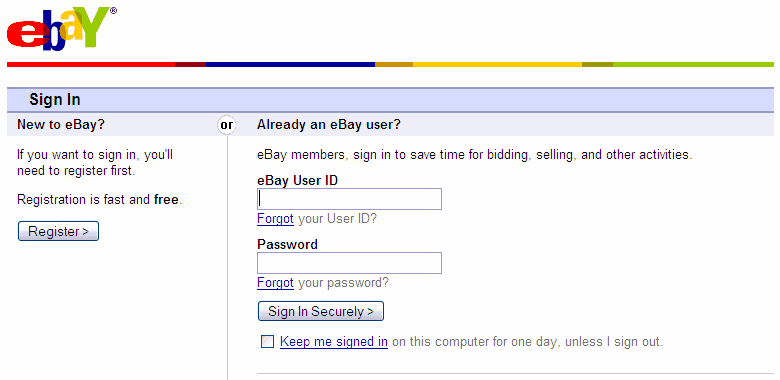
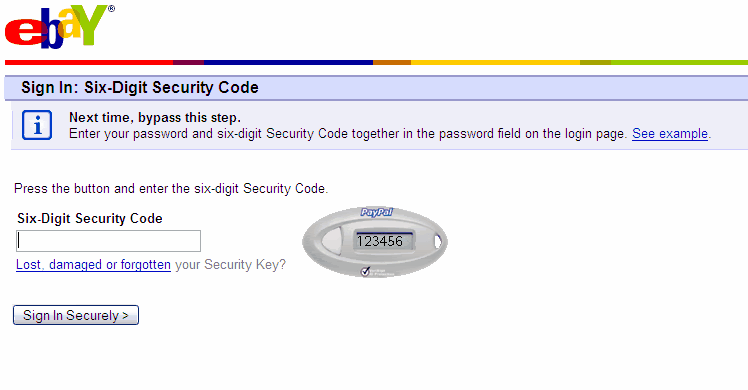
If an eBay/PayPal member obtains the "PayPal Security Key", the member must activate it on either PayPal or eBay and must register the unique alpha/numeric serial identification number on the back of the key. The member would then also activate the "PayPal Security Key" on the other platform. To use the key on both PayPal and eBay, the member has to log on with his user ID, password, and input the 6-digit number that is randomly generated by the "PayPal Security Key". Once the member successfully logs onto PayPal or eBay he can fully access his account. Members do not need to log into eBay and use the key if they only wish to surf eBay.

The unique alpha/numeric serial identification number on the back of the "PayPal Security Key" is solely assigned to the PayPal/eBay account for a specific person or business. Presently, only one PayPal account can be associated to one eBay account; therefore, if a member has a combination of two or more PayPal/eBay accounts, each PayPal/eBay account would require its own "PayPal Security Key".

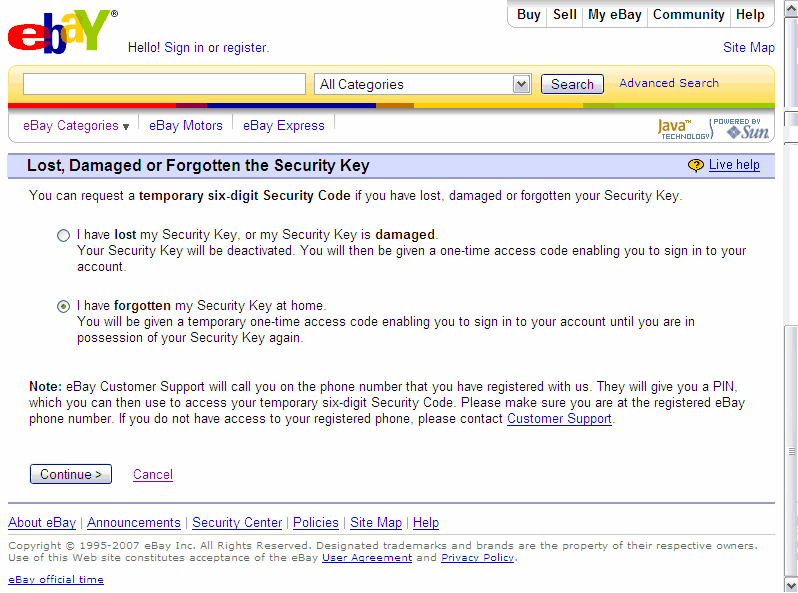
If a "PayPal Security Key" is lost, it is of no value to anyone else because the alpha/numeric serial identification number has already been registered with PayPal/eBay and cannot be reassigned or transferred. Should the key become faulty or is lost, the "Paypal Security Key" will be disabled by PayPal/eBay once the member it is assigned to reports such to PayPal/eBay. Members who may leave their "PayPal Security Key" at home, while wanting to access their PayPal/eBay accounts from another location, and those who are waiting for a replacement "PayPal Security Key" are still be able to access their PayPal/eBay accounts, but must answer security questions of which the answers are only known to them. Hijackers are unable to gain access to any PayPal or eBay accounts that are activated with the "PayPal Security Key" because the hijackers are unable to successfully answer the security questions.

The bottom line is that hijackers cannot tamper with PayPal/eBay member accounts that have activated the "PayPal Security Key".

Click on the thumbnail images below to enlarge them for a visual illustration of the PayPal and eBay log on pages when the "PayPal Security Key" is activated.
On a side note, we would like to mention that the estimated life of the battery in the "PayPal Security Key" is approximately one to two years. The battery cannot be replaced, so a member must obtain a new key from either eBay or PayPal.

We suggest that both PayPal and eBay create an icon that will appear as follows:

PayPal

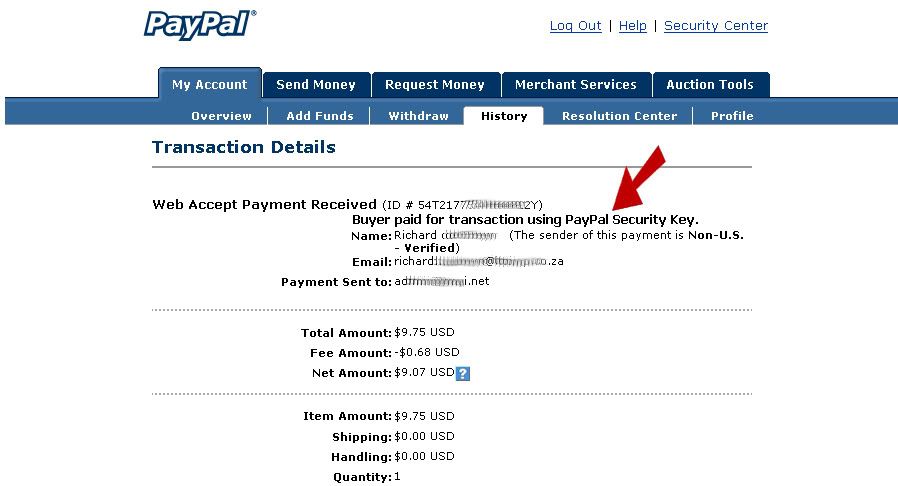
• The new icon will appear on the PayPal message sent to the seller that the buyer accessed his PayPal account by using the "PayPal Security Key" and has paid for the transaction.

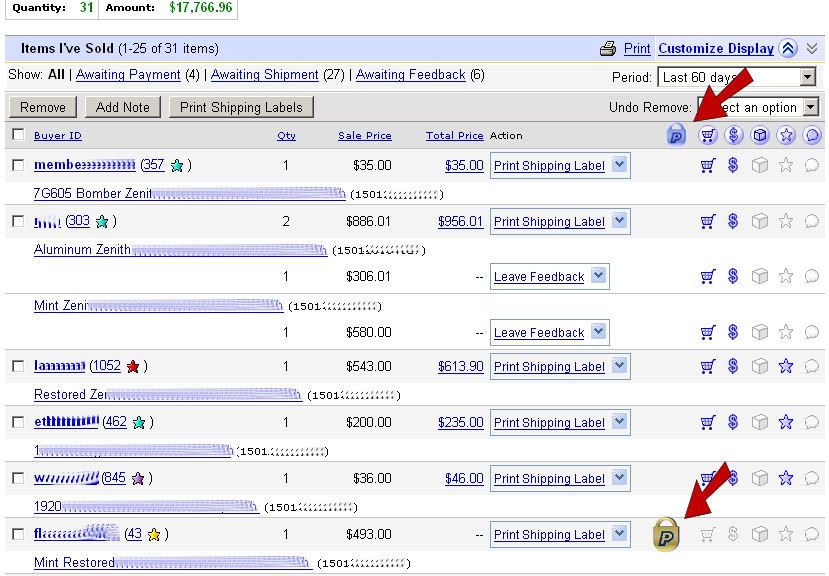
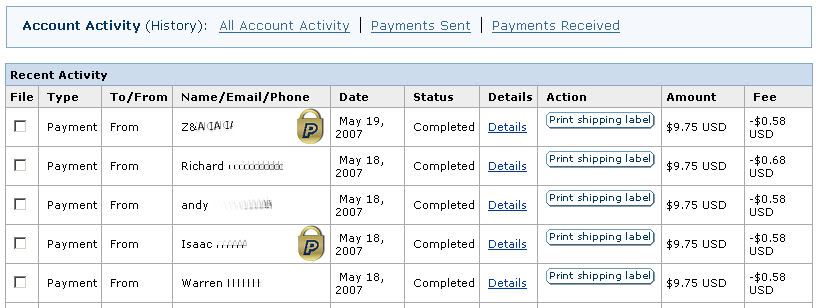
• The new icon will appear in a new column on the PayPal transaction register only for transactions in which the "PayPal Security Key" was used.

By implementing this new icon in these locations, it will give the seller confidence that the buyer did indeed authorize payment for the transaction. Although thieves can copy and use the icon in spoof messages, users will be able to verify the authenticity of a payment/receipt by accessing the transaction register on their PayPal accounts.

Click on the thumbnail images below to enlarge them for a visual illustration of the proposed changes to PayPal.


eBay

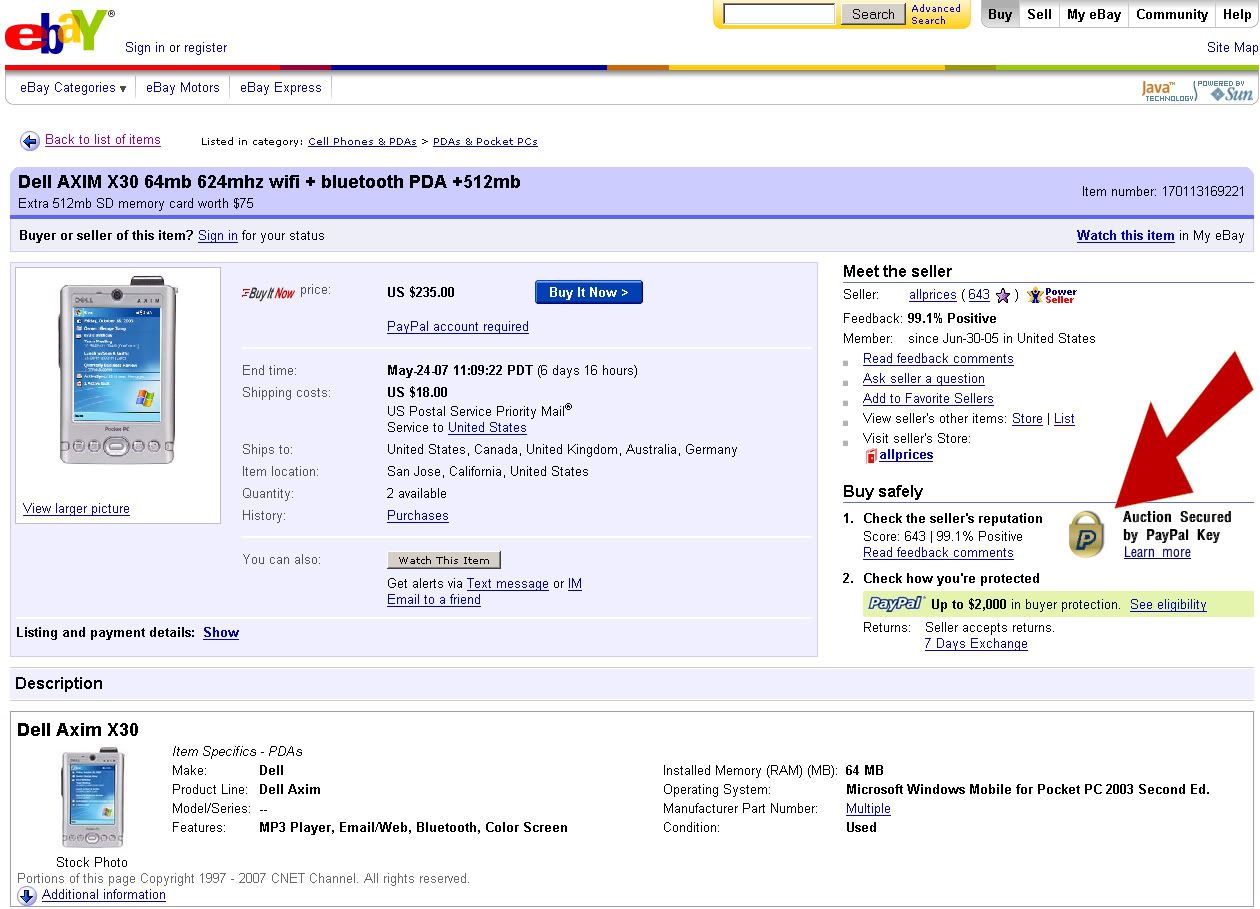
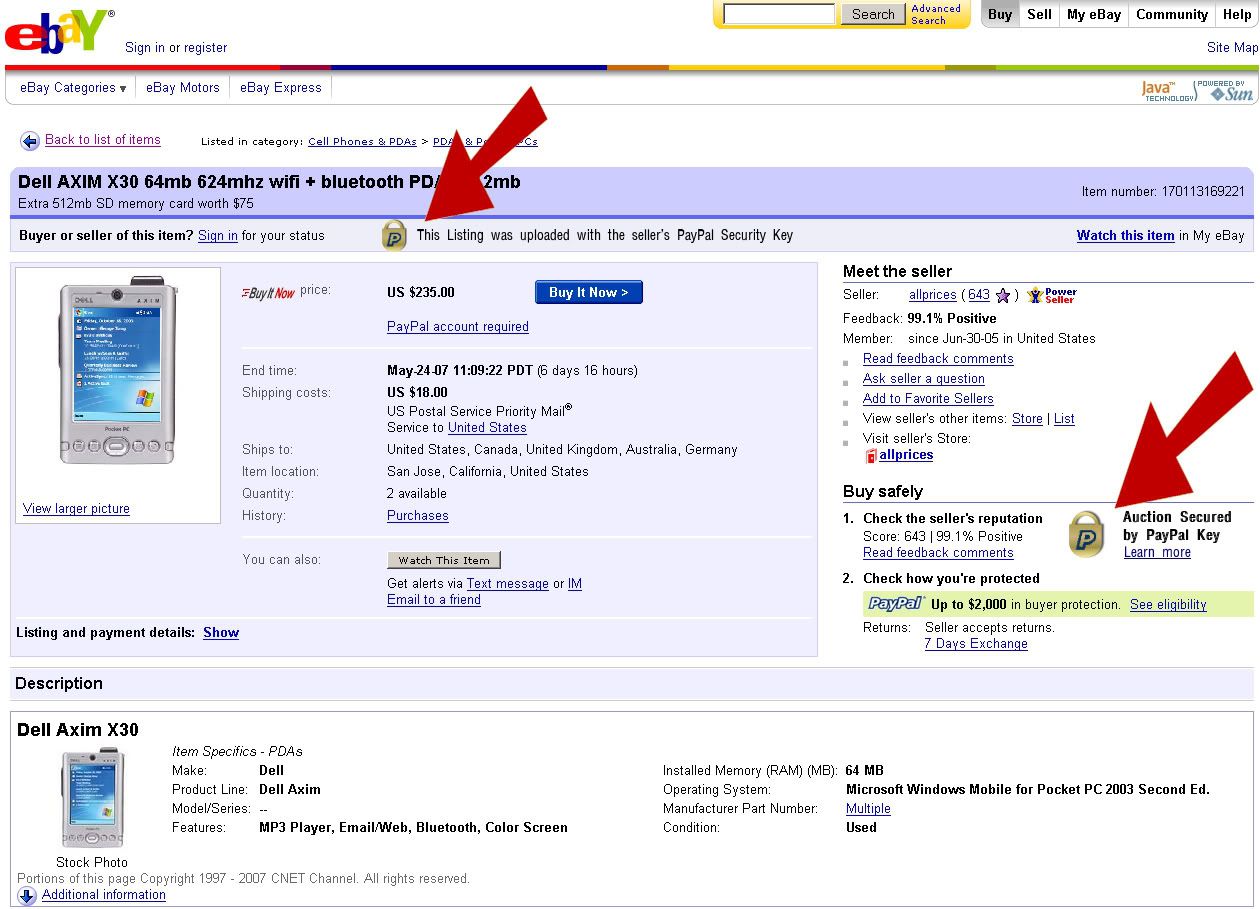
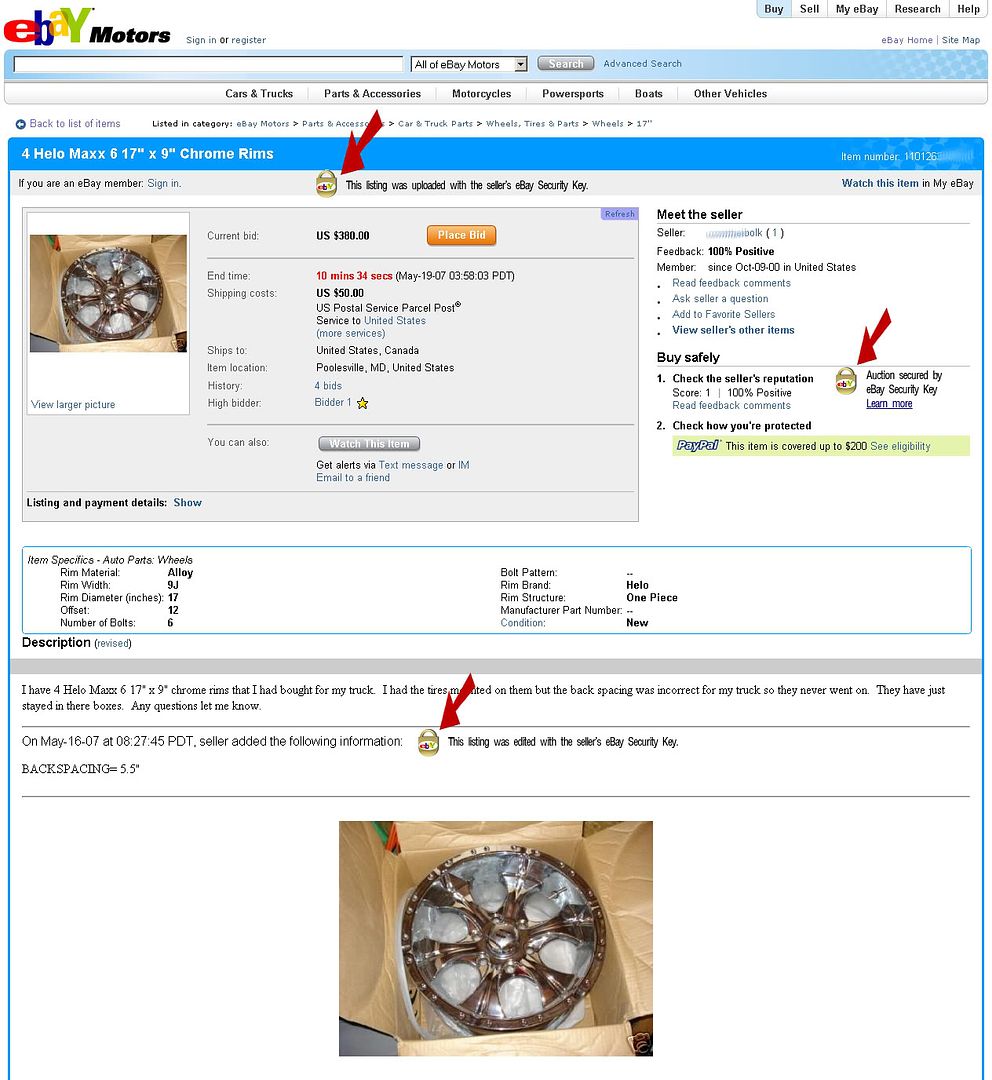
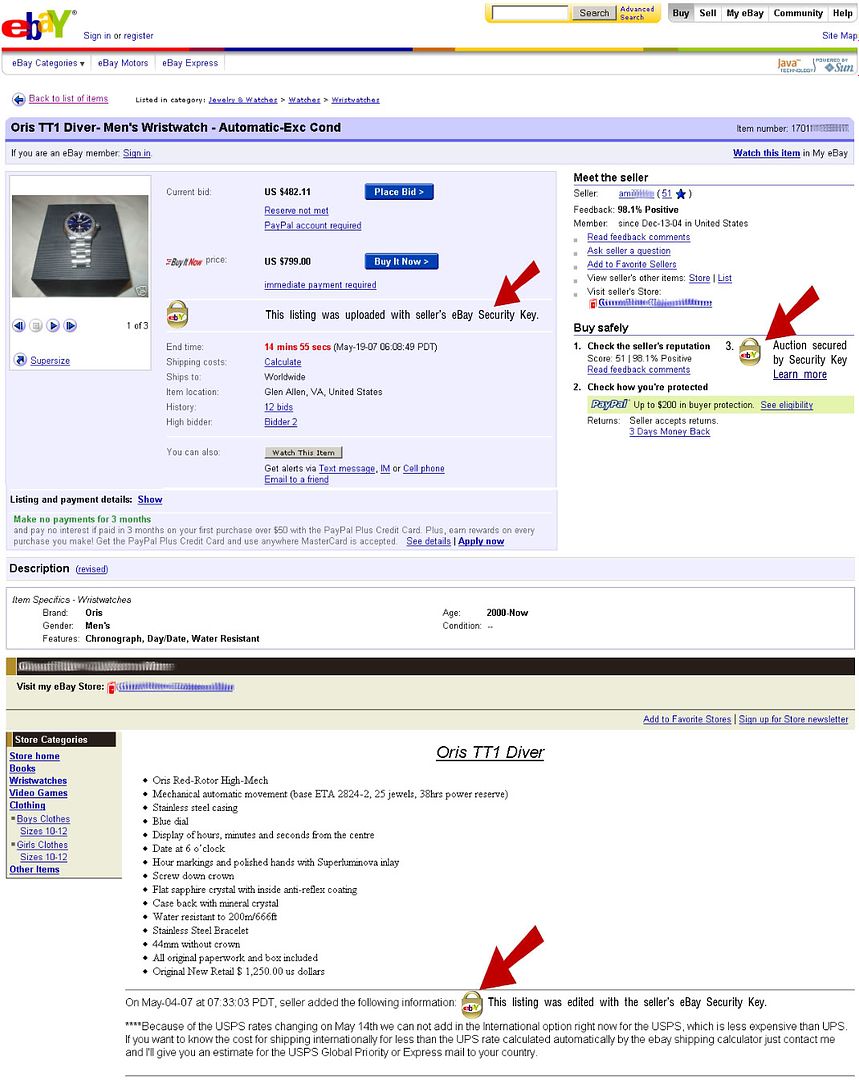
• Listings that are created and uploaded onto eBay platforms where the seller has logged in to his account with the "PayPal Security Key" will display the key icon in the blue listing box and in the location where the PayPal buyer protection information is located. It will also be necessary to use the "PayPal Security Key" to upload listings through Turbo Lister and any other third-party programs.

• If an existing listing that displays the key icon is revised, the eBay member must log in to access his eBay account with the "PayPal Security Key". If the member does not log into his account with the "PayPal Security Key", he will be unable to revise the existing listing. The member also will be unable to cancel the listing by himself. The member will have to contact eBay's Live Help for Fraud group to have the listing canceled and will also be required to provide verification information to the Live Help agent. eBay will not refund the listing fee to the member, as it will be considered canceled and not TKO'd. The eBay member will be able to list items without the key, but the "PayPal Security Key" will not appear in the listing. By only allowing members to revise listings with the "PayPal Security Key" this further prevents hijackers from accessing accounts and revising genuine listings for their own illegal benefit.

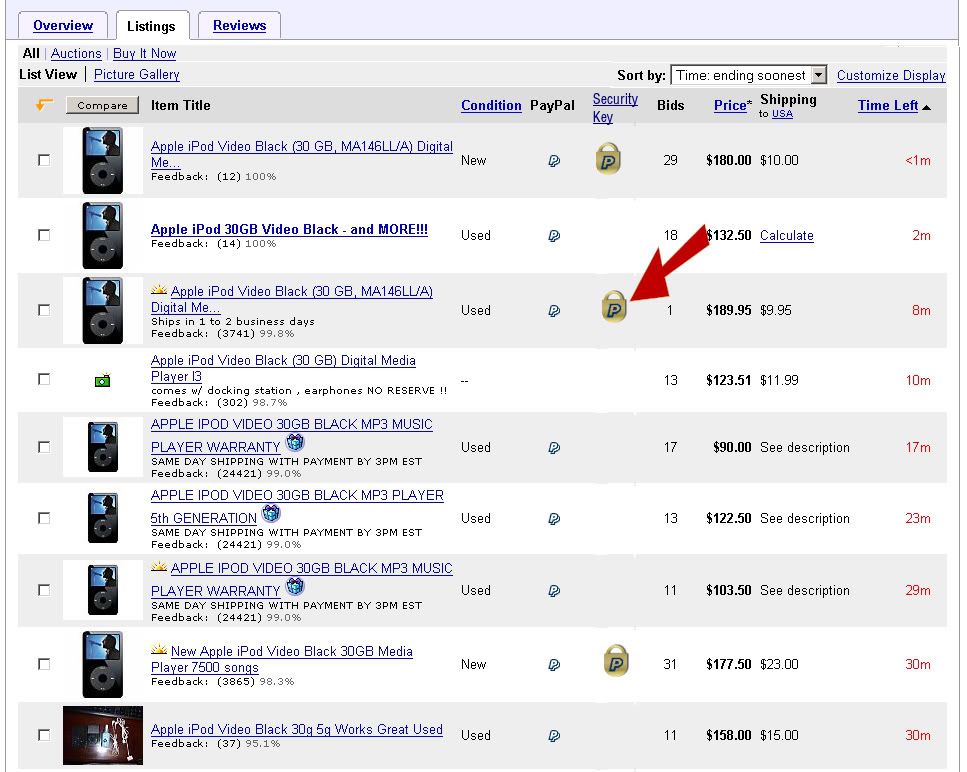
• The key icon will appear for all listings that are uploaded with it in a column on the eBay search results page.

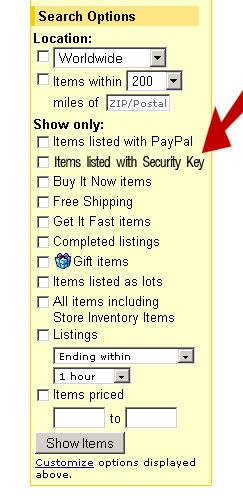
• Just as members may search for listings that have PayPal as a payment option, the key icon will be added as a search function on the left hand side of the search page.

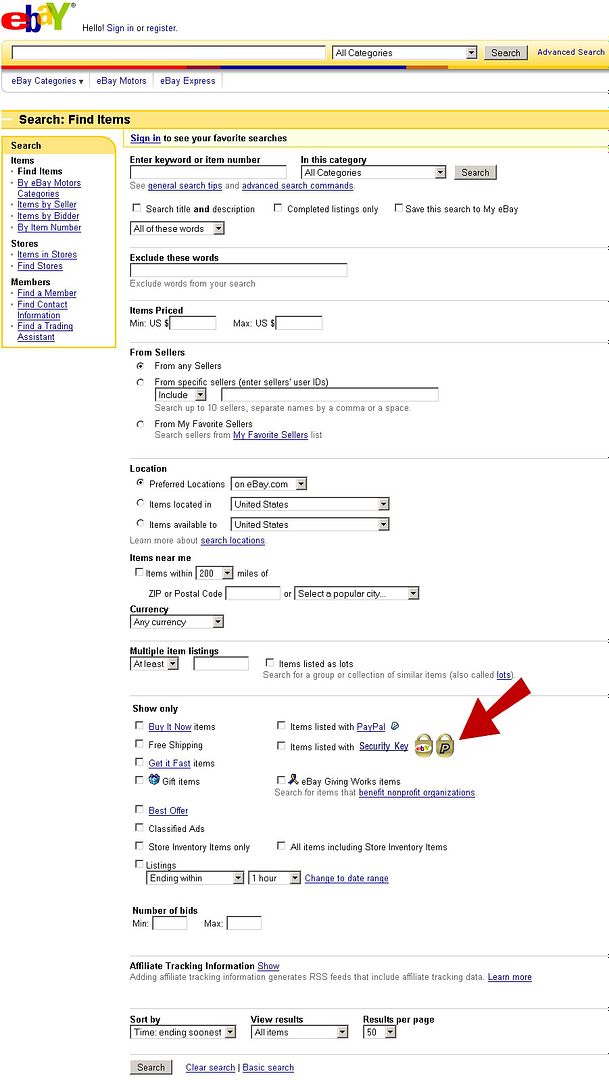
• The key icon will be added as a search function on the Advanced Search screen.

• The key icon will appear on the My eBay Summary screen for all applicable listings sub-categorized under "All Buying" and "All Selling" that are uploaded using the "PayPal Security Key" and paid for through PayPal with the buyer's "PayPal Security Key".

• We also suggest that because PayPal is not accepted by every seller, available in every country, or available to every member, that on eBay's platforms the key should be renamed the "eBay Security Key". eBay should also add its own logo to the existing key (which only says "PayPal") or create a key solely with the eBay logo on it.

Click on the thumbnail images below to enlarge them for a visual illustration of the proposed changes to eBay.
eBay Member Confidence

• eBay members will have confidence in these specific eBay listings, as they can only be uploaded to eBay platforms by the true member that is assigned the "PayPal Security Key".

• Buyers will have more confidence that listings are genuine because they will be able to search for listings containing the "PayPal Security Key."

• Buyers will continue to have confidence when obtaining general search results. They will be able to immediately see the "PayPal Security Key" icon related to each item and know, without having to click on the listing, that the listing is genuine.

• Instilling buyer confidence in eBay listings will generate more sales and higher sales dollars for sellers that use the "PayPal Security Key," and will also increase the average selling price (ASP), final value fees and increase revenue for eBay.

• Should an eBay member be assigned and have in his possession a "PayPal Security Key" and then be NARU'd, eBay will automatically disable the key for all eBay accounts associated with that particular key until the member is again in good standing. PayPal accounts will remain unaffected. However, because eBay and PayPal are considering allowing the "PayPal Security Key" to be used for multiple accounts in the future, this safety mechanism will prevent NARU'd members from having the opportunity to log in to eBay with the key.

• The more exposure the "PayPal Security Key" icon receives through eBay marketing, promotion, and announcements, the more it will convince other members, and specifically, sellers to obtain the "PayPal Security Key" for their own use.

Site Key

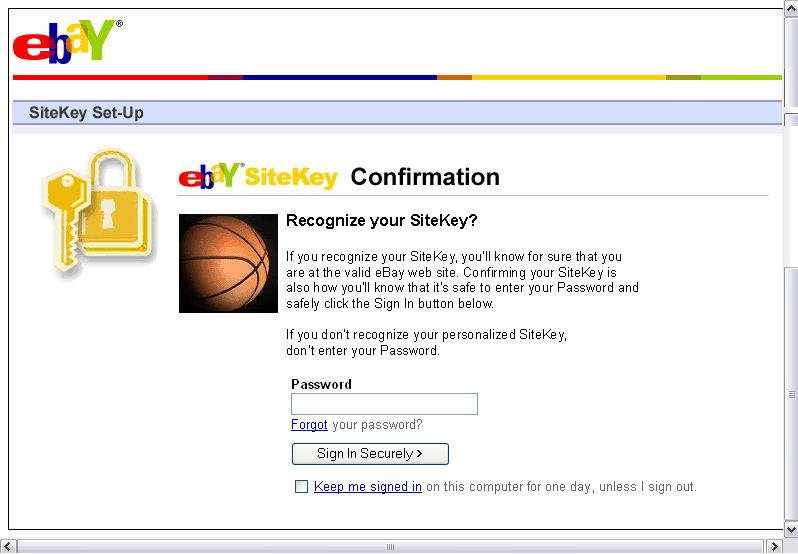
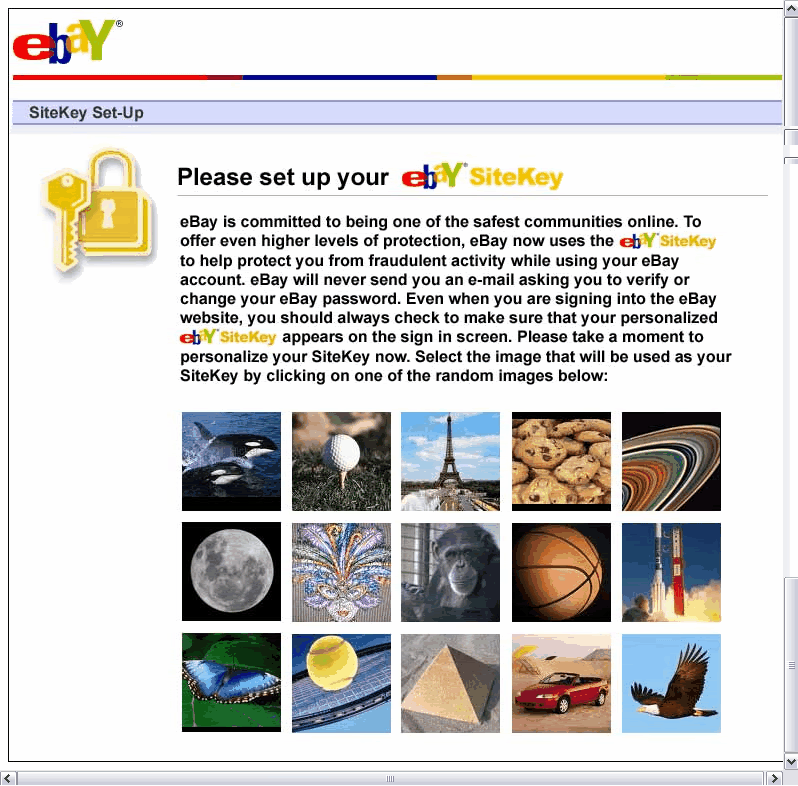
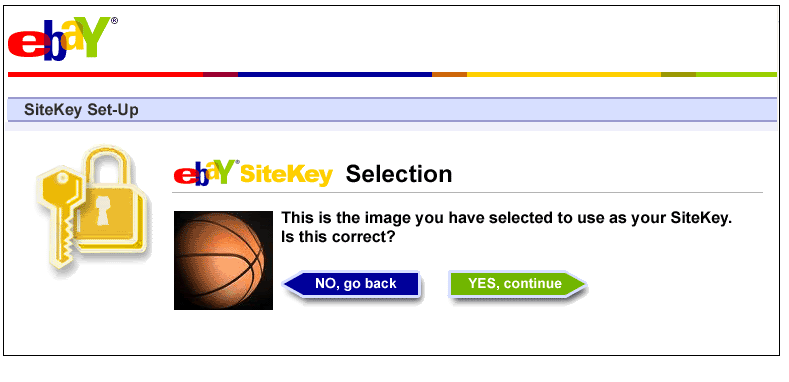
There may be some eBay members that infrequently use eBay, and therefore, might find the added security by using the "PayPal Security Key" to be cumbersome or not worth the $5 investment. Therefore, we suggest that to accommodate these eBay members and to provide further security, eBay also implement a site key.

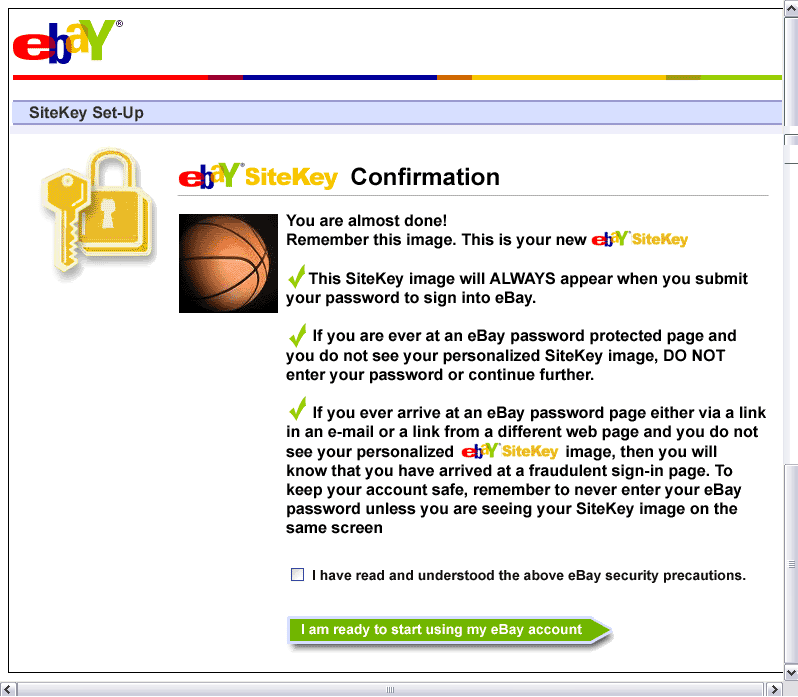
A site key is a small image, chosen by the member to "individualize" his account. Each member will select an image from a random array of 50 images, and set up a security question. Each time a member logs in to his account, after entering his user ID, he will be directed to a second screen showing a random set of images. The member must choose his preselected site key and input his password to complete the login process. If the member does not choose the correct site key, he will be allowed a second attempt. If again unsuccessful, on the third attempt he will be asked to answer the security question. If the security answer is incorrect, the account will be completely disabled for 4 hours. The member will be sent an email message addressed to his eBay registered email account notifying him of the three unsuccessful attempts to log in to his account, and that the account is disabled for 4 hours. The email will also provide instructions on how to contact Live Help for assistance to have the account reactivated, though no action will be required by the member if he did not access his account and if he can wait through the 4 hour disablement period.

• The security question choices will be out of the ordinary. For example, questions with common answers will be easy to guess at. However questions such as "What is your eldest sibling's middle name" and "Name your first employer" will be nearly impossible for a thief to answer.

• Site key images will always appear in random order, and because the member will have two attempts to select the correct image to log into eBay prior to answering the security question, hijackers will be unable to determine which image is correct through keylogger programs.

• We further suggest that eBay create a library of 3000 site key images to choose from, although it only needs to offer a member an array of 20-30 images to choose from to initially activate the site key account protection. By implementing the site key and security question precautions, a hijacker would be unsuccessful in leading a member to a fake eBay login page.

• Since we are aware that there are millions of dormant accounts in eBay's database, we suggest that if a member has not activated either the "PayPal Security Key" or the site key within 30 days of the site key being rolled out, that eBay temporarily disable such accounts and require verification of membership when accessed. In the alternative, at a minimum, eBay should disable the selling privileges on the dormant accounts so hijackers already having access to an undetermined inventory of user IDs and passwords are unable use the dormant accounts to create fraudulent listings for their own purposes.

Click on the thumbnail images below to enlarge them for a visual illustration of the proposed changes by adding a site key.
Email Messages, Hyperlinks and Member Registration

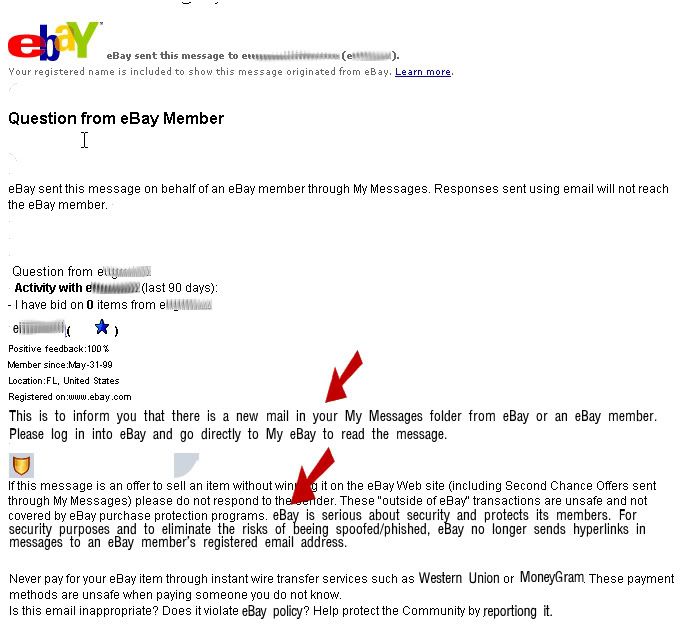
• Both eBay and PayPal will remove all hyperlinks from its messages and only send messages to members stating they have new messages to read in the My eBay My Messages/PayPal accounts.

• By removing hyperlinks from messages and educating its members that neither eBay nor PayPal send email messages with hyperlinks, members will learn that any messages that look like they appear from either eBay or PayPal with hyperlinks in them are spoof and phishing attempts to obtain member IDs and passwords. By removing hyperlinks and educating members, the members will be less likely to be spoofed or phished, and thus not give up their private information.

• eBay will no longer allow members to register member IDs that are at all similar to their eBay registered email addresses. In this way, members will be less likely to receive fake Second Chance Offers from scammers who use random generator matching programs to detect member email addresses for their scams. This is extremely important because eBay's SMI initiative only obscures member IDs when a listing with bids reaches the $200 threshold.

• eBay will no longer expose any member's email address in Ask the Seller a Question and member to member messages. eBay will allow sellers to answer bidder questions that request additional images by creating eBay generated disguised links through the eBay messaging system similar to the way TinyURL works. Furthermore, eBay will perform malware scans on the links and images to ensure that neither the links nor the images are infected. Bidders wishing to see the images will click on the links to view them.

Click on the thumbnail image below to enlarge it for a visual illustration of the proposed changes to email messages.


If eBay requires its members to either use the "PayPal Security Key" or the site key, thieves will be unable to hijack eBay member accounts and existing listings, therefore, thieves' activities will be limited to the listings on the brand new accounts they create for themselves.

By implementing the above security processes as a complete package, eBay gives its members options, along with offering true security and assurances, that listings on its platforms are created by the true account holders and not hijackers. Member confidence in eBay being a safe marketplace will increase, members will be able to properly evaluate other members through feedback, the public's perception of eBay will be positive, and eBay will be proactively taking action to combat fraud on its platforms. Transparency will return to eBay's platforms.

Implementation of the security processes will allow eBay employees assigned to removing fraudulent listings, securing accounts, and assisting members with fraudulent activity due to hijackings to spend their time doing better things than repetitively removing listings, securing accounts, and advising its members how to keep their accounts secure. eBay's Trust & Safety team will become more effective and have the manpower and opportunity to concentrate its efforts on the problems with the Chinese counterfeiters, shilling violations, and other important trust and safety issues.

By no means will these security processes eliminate all of the fraud on eBay, however, it is a step in the right direction and a way to remove most of the fraudulent listings from eBay's platforms, while keeping its venue status, and protecting its members. We urge eBay's and PayPal's management teams to evaluate these security processes and implement them immediately.

The Nekkid Truth blog thanks the administrator of the Company Exposed website, eBay member "thepursesboutique", Team Whack a Hack, and the many eBay members wishing to remain anonymous for collaborating on this blog entry and providing the illustrations.

For press/media contact, please write to the blog administrator at always.the.nekkid.truth@gmail.com. We welcome all reader comments and questions. Please feel free to post your comments directly to the blog or email always.the.nekkid.truth@gmail.com for further information.
***NOTE***

We believe that we are proposing viable security solutions that eBay can easily implement, which will benefit eBay and its members. On Sunday, May 20, 2007, email messages were sent to eBay executives Bill Cobb, Philipp Justus, Rob Chesnut, Matt Halprin, and Dave Cullinane requesting that they review the proposed security suggestions and respond to this blog entry (see email message below). We will keep our readers updated and let you know if and when we receive a response from eBay.

Date: Sun, 20 May 2007 12:04:18 -0700 (PDT)
From: "The Nekkid Truth"
Subject: Security Proposal to Reduce Fraudulent Listings on eBay's Platforms
To: billc@ebay.com, pjustus@ebay.com, robc@ebay.com, mhalprin@ebay.com, dcullinane@ebay.com
CC: ina@auctionbytes.com

Dear Messrs. Cobb, Justus, Chesnut, Halprin, and Cullinane:

A group of eBay members that have been critical of eBay's lack of security have taken it upon themselves to find solutions to reduce fraud, and increase security and member confidence on eBay's platforms. Implementation of our proposed security enhancements are solutions to the issues eBay faces daily, and, will ultimately increase sales and revenue on eBay. Please review the proposal posted at http://nekkidtruth.blogspot.com/2007/05/ebay-members-crying-out-for-better.html.

We believe your IT group is technically capable to write the required code and perform the beta testing in order for these security enhancements to be implemented on eBay's platforms prior to the Christmas 2007 listing/buying season.

Further, by implementing these solutions, eBay returns transparency to its marketplace. Our proposed security solutions have merit and not only will solve eBay's security and fraud issues, but will strengthen eBay and give eBay members confidence in eBay. This is a win/win situation for eBay.

If you are in favor of implementing our proposed solutions this would be a wonderful announcement you can make at eBay Live. eBay's upper management will be getting the message out to a very large audience that it is proactively pursuing solutions to increase security and reduce fraud on its platforms.

We welcome your comments.

Sincerely yours,

The Nekkid Truth Blog

Company Exposed

Team Whack a Hack

Anonymous eBay Members

Friday, April 20, 2007

eBay Town Hall Meeting on April 30, 2007 - Trust & Safety Issues to be Discussed


Based on the following announcement, it doesn't appear that eBay wants to create a thread on its Town Hall Forum message board for members to post questions. eBay would prefer to privately receive email so the panelists can quietly select the questions they want to answer.

***Phone In Your Questions! Town Hall with Bill Cobb on Monday, April 30th***

April 19, 2007 | 12:10PM PST/PT

Hi everyone...this is Bill Cobb, President of Marketplaces North America. I'd like to invite you to my next Town Hall event on Monday, April 30 from 2:00 p.m. to 3:30 p.m. Pacific time. This month's topic is Trust & Safety.

My friend and colleague Rob Chesnut, eBay's Senior Vice President of Trust & Safety, along with several members of his team, will be joining me during this Town Hall. I'm also pleased that eBay's Chief Information Security Officer, Dave Cullinane, will be able to join our panel. Dave brings 35 years of experience in the information security business to our team, and we're delighted to have him.

Ask us your question on the air
We'll be broadcasting LIVE via Internet radio with the help of our friends at wsRadio. If you have a question for me, Rob, or one of the other leaders on our panel, you'll be able to call us at our toll-free number – 877-474-3302 – to talk to us about your Trust & Safety question in person.

As always, you'll be able to listen in via Windows Media Player or Real Player.

Email us your question before the Town Hall
If you’d prefer, you can also email your Trust & Safety-related question to us before the event to TownHall@ebay.com – we’ll be answering some of our email during the show, as well.

So, I hope you'll join us. Visit www.ebay.com/townhall for all the details.

Sincerely,

Bill Cobb
President, Marketplaces North America
From past experience, the panelists, and specifically, Bill Cobb and Rob "Pinocchio" Chesnut, most likely will not be forthcoming and answer the tough questions about fraud on eBay's platforms. Cobb and Chesnut will probably continue to tout the success of eBay's SMI initiative and state that fake second chance offers and shill bidding are practically non-existent. eBay members know differently ~~ SMI has bombed and it only protects the identities of shill bidders.

We would like to know what questions you are posing to the panelists. Send a copy to always.the.nekkid.truth@gmail.com and we will post your questions on the blog (out of courtesy to you and for your own protection, we will omit your email address). Even if eBay doesn't believe in transparency, we do. After the Town Hall Meeting transcript is released, we will then know exactly which questions the panelists chose to answer.

Tuesday, April 3, 2007

eBay's Public Image ... Does it not care about its reputation?


Do you get a warm and fuzzy feeling when you think about eBay? Or do you think of eBay as a rapist's accomplice? If you have been ripped off because you entered into or thought you entered into a legitimate transaction on eBay, you feel violated and most likely think the latter. If you are a victim of eBay fraud, you have every right to hold eBay partially responsible and accountable for its actions. If you have been led to believe that eBay is a safe place to transact business on and that eBay is doing everything it possibly can to combat fraud on its platforms, you are sadly mistaken.

A recent Google search of the phrase eBay scam provided 3.1 million results.

eBay used to be known as a website for being able to find unique, hard to find items and it was fun to surf through the listings. Now, this Internet giant, protected by its venue status is known as a website where it allows thieves to hack honest member accounts (by phishing/spoof emails and redirects) or allows them to create their own fraudulent accounts and use its servers to list tens of thousands of bogus listings each day. And, let's not forget that eBay allows a multitude of thousands of Chinese accounts on its site that are either selling illegal knockoffs or else they are making attempts to get honest members to act as money mules. These examples of fraud are only the tip of the iceberg.

Does eBay care? Absolutely not. This is a multi-billion dollar, multi-national company that does not have a conscience. eBay has grown too big for its britches and its arrogance is apparent every moment of the day. eBay is not a good member of the vast Internet commerce community. eBay's perception is that it is omnipotent.

On Thursday, March 29, 2007, eBay hosted a 90 minute Town Hall Meeting, and members were either invited to post their questions at eBay's Town Hall Forum message board on a thread entitled March 29 Town Hall Question Thread or call in. To hear the rebroadcast from the March 29, 2007 Town Hall Meeting, click here.

Bill Cobb, President of eBay North America and other management personnel were the panelists that answered questions. Members were informed in advance that not every question on the thread would be answered. However, what was most surprising is that members that called in to the live Town Hall Meeting not only had their questions pre-screened, but many were intentionally hung up on if the questions being posed to the panelists were related to fraud. The members that called in had legitimate concerns they wanted addressed, yet eBay treated each of these people as if they were childishly making prank telephone calls, and the only solution eBay had was to hang up on them. This is not the way for a corporation to treat its members. This action further cements eBay's arrogance and proves that eBay's management team has absolutely no respect for its users. eBay's Board of Directors and investors should be ashamed of eBay's management team.

Following are many of the questions from the thread cited above that were not addressed by the panelists during the live Town Hall Meeting:

Why is Google checkout not an accepted means of payment on eBay?

Is anything going to be done about the auction listings that have a super low starting price and then add shipping charges which are clearly double or triple what they should be?

What do you feel are the motives behind the recent Vladuz hackings, and do you personally maintain that company line that he never breached your security? If so, how do you explain his last two "hackings" where he took over control of eBay employees' accounts? If, as management's spokespeople have stated, he gained access to eBay servers and databases for employees only via employee email accounts, have these employees been dispatches appropriately?

Vladuz recently alluded to an interview with CNN (on March 15th, I believe)....he then later emailed certain people and said that the interview was off. Did eBay contact CNN and threaten to sue if such an interview was done? If so, did eBay contact corporate at CNN or just intimidate the reporters involved?

How were some scammers who listed dozens, hundreds or thousands of auctions allowed to keep listing even after becoming NARU'd?

Why was eBay unable to remove certain scam auctions from the site for hours and sometimes days after the user became NARU'd?

Last year you spoke of increasing customer service....yet we users have yet to see any sort of increase in the amount of customer service, nor have we seen better means of CS, quicker response times or less canned emails.

So, is that a result of you simply lying to customers or is it a case of poor management? If so, who's dropping the ball?

When is ebay going to take the quite necessary step IMO of requiring significant identity verification of all new users? Will this ever happen?

When is ebay going to step up and better educate new users as likely the only way to help control the incredible rash of hijacked accounts and users who are being scammed on a daily basis? Will this ever happen?

When will ebay, instead of merely telling potential customers that "feedback will keep them safe", take the also necessary step and ban 1 cent BIN and other auctions that can only result in a seller losing money in listing fees and thusly are obviously designed for no purpose other than to manipulate that system to the detriment of users? Will this ever happen?

We know that eBay has a tenuous relationship with instant money transfer services such as Western Union and Money Gram. Why doesn't eBay instead attempt to have an amicable working relationship with these companies, and work together to stop the transfer of funds to criminals?

How many fraudulent listings are TKO'd by eBay each week due to hijackings and fraudulently created accounts? How many accounts does this consist of on a weekly basis?

Thieves are now creating accounts on eBay Express and then listing on eBay. Are the same requirements necessary to register for both platforms?

Does eBay verify credit card, debit card, and banking information prior to allowing listings to be uploaded on its platforms? Besides matching account and routing numbers, is eBay verifying the name on the account?

Why is eBay not requiring thorough buyer education for all newly registered members? It should be mandatory to take and pass tutorials before having the ability to buy and sell. For that matter, eBay should require members to take refresher tutorials every 60 days.

eBay's T&S groups use third party intrusion detection software to determine if an account has been hijacked when reported via webform or to Live Help. Why is eBay not running this software 24/7/365 on all listings being downloaded onto eBay's platforms?

It was recently reported that 23% of all registered eBay members have been inactive for 1 year or more. Why is eBay not putting those accounts in suspense so that the hijackers don't have the ability to use those accounts and cut off the inventory? If an account is inactive for a minimum of 30 days, it should be suspended. The registered user can then answer the secret question to reactivate the account.

We know that FADE does not work well, so why doesn't the T&S group set up RSS feeds for specific key phrases and hijacker email addresses to find the fraudulent listings, fraudulently created accounts and hijacked accounts quickly instead of relying on the community to report them?

When is eBay going to eliminate penny listings?

Why doesn't eBay reprint the "category" a listing is in within the description in a large bold font so that members can easily see where the item is located in? The tiny font above the listing is barely noticeable. If members were more aware where the listings were located, believe me, it would put many of the thieves that hijack accounts out of business.

Why is eBay not sending out a monthly educational email to all members regarding how to protect themselves from fraud on eBay just like Overstock does?

When is eBay/PayPal going to remove all links from email messages and instead send out an email to say to check My Messages for email? This would certainly cut down the number of spoof and phish email messages.

When is eBay going to begin to enforce a detailed verification process for developers to insure that they aren't hackers? If I were going to allow developers to have access to my server, believe me, I would check them out and also make them secure a financial bond.

Why does eBay allow certain notifications to be turned off in Preferences? If members were required to receive listing and selling notifications to registered email addresses, they would know immediately if their accounts were hijacked. For that matter, why doesn't eBay have a similar notification for listing changes? In February thousands of listings were hacked by at least one thief with a contact message for Buy It Now. Had members who had their listings hacked by this thief been notified through eBay's message system, the members would have been able to take action.

Why is there not a warning message on the log in page to remind all members to not use instant money transfer services? This message should be in a large bold font.

Why is eBay not in contact with manufacturers to learn the release dates of items? The Nokia N95 cell phone was not available for sale until the end of February/beginning of March, yet thieves were listing the phone for sale as early as September. The same goes for the Apple I-Phone. It is being listed now by thieves, yet it will not be available for sale until at least June. eBay should not be allowing these items to upload until they are actually available for sale.

When is eBay going to begin taking a proactive stance towards fraud instead of a reactive one?

Why can unverified Chinese sellers list 1000's & 1000's of fraudulent designer named items w/o any problems BUT long standing UK & US sellers of authentic designer products suddenly be limited/banned from listing (sometimes indefinitely) even after they provided documentation proving the merchandise to be authentic?

When is eBay going to create a policy to not allow members to sell email addresses on its platform? The email providers such as gmail, AOL, Hotmail, Yahoo, etc. allow people to create them for free. Is eBay that greedy that it needs to make a profit from things that are free?

Are you gonna stick store sellers with another fee increase for 2007 or start charging them extra for Ebay Express exposure?

Will eBay consider make public how it calculates fraud? We would like to know the number of listings that are taken down because of hijackings/hackings and how many accounts are involved on a monthly basis. We would also like to know these numbers by listing category (note the numbers by category might not be accurate because thieves list items in the wrong categories). We know that listings from hijacks/hacked listings are not part of eBay's fraud calculation (and that you only base the numbers on claims) and therefore we would like to see fraud reported differently by eBay.

Approximately, what is the length of time it takes for eBay to secure an account from the first webform report it receives? A 2-hour window to me seems sufficient.

Mr. Cobb, will you, Meg Whitman and Rob Chesnut voluntarily agree to not accept your quarterly/annual bonuses if you cannot minimize the hijackings/hackings of accounts by at least 50% from the previous year? As a senior executive, we would like to see you be responsible and accountable instead of giving the community lip service.

What actions has eBay taken to protect users from the trojan.bayrob bug?

Will Mr. Cobb answer questions about scams, fraud and the general lack of security on eBay or does he just want soft questions to give the impression that all is well with eBay?

Why is Ebay not alerting users when their eBay accounts are compromised and their personal information is posted on the community boards?

The following question from the thread cited above was answered at the Town Hall Meeting, however, Bill Cobb, President of eBay North America had absolutely no idea that an announcement that he publicly made on January 17th, with an effective date of the same day has not been implemented. Currently, there is no proposed date for the policy to go into effect, and eBay doesn't even know if it is even possible to implement the policy. The second part of the question went unanswered.

I am finding newly registered members that are selling not accepting PayPal, however it was announced on January 17, 2007 that all newly registered members that are selling must accept PayPal effective January 17, 2007. The categories I found listings in were not exempt (Motor Vehicles and Mature Audience) from this policy.

Please advise why the policy below has not been implemented, and why there are no change notices on the site stating it has not been implemented?


Announced January 17th, 2007 by Bill Cobb

Safe Payment Requirement for New Sellers
- Today I announced that we'll be requiring all newly registered sellers to accept PayPal or a merchant credit card. We know that PayPal is the safest way to pay on eBay, and we want to make sure our buyers have this option with new sellers. (Existing sellers will not be affected by this requirement.). (Read our FAQs for more details.)

Here is the link: http://www2.ebay.com/aw/core/200701.shtml

http://pages.ebay.com/help/announcement/25.html#question4

What is the Safe Payment Requirement for New Sellers and what does eBay consider to be a safe payment method?
eBay will require new sellers offering items in most categories to buyers in the U.S. and Canada to provide at least one safe payment method. Safe payment methods include PayPal or a Merchant Credit Card. These safe payment methods must be included as an available payment method on their listings. New sellers may also include any of the other accepted payment methods on their listings. (See the Accepted Payments Policy for more details on accepted payments.)

eBay strongly encourages sellers to offer payments through PayPal – PayPal is not only convenient to use, but it also offers buyers and sellers industry-leading protection against fraud, chargebacks, and theft of financial data. Merchants with their own Merchant Credit Card processing account, and those who use a third-party credit card processor, may offer their buyers the option of paying directly with a credit card online (including through third party checkout) or by phone in addition to or instead of PayPal.

Who is affected by the Safe Payment Requirement for New Sellers and when will this requirement go into effect?
All members registered on or after January 17, 2007 who wish to list items will be affected by this requirement. Certain categories where these payment methods often are not practical, such as Motor Vehicles and Mature Audiences, will be exempted.

http://pages.ebay.com/help/sell/seller_account.html

Step 3. Offer PayPal or a Merchant Account Credit Card as a Payment Method
To keep eBay a safe place for both buyers and sellers, sellers who register after January 17, 2007 are required to offer either PayPal or a merchant account credit card as an accepted payment method for their items. PayPal allows you to accept credit card and electronic check payments online from your buyers. You can sign up for PayPal before you list your first item for sale, or you can sign up when you list your first item.

Secondly, do you realize by not having this policy implemented you are still continuing to allow these bogus scam artists to create accounts and list their phantom, non-existent items? Do you understand that the T&S webform team and Live Help for ATOs is hesitant to shut down these accounts when reported because there are not any third-party intrusions?

Why did the President of eBay North America make this announcement on January 17, 2007 not only in a message posted on eBay's General Announcements but also at the eBay eCommerce Forum? And, as captain of the eBay ship, why did Bill Cobb not know until two and a half months after making the announcement that a policy initiative that he personally announced has not been been implemented? Is Cobb at the helm of eBay or asleep at the wheel? If he is asleep at the wheel, then eBay North America will soon sink like the Titanic.

We also believe that the reason this policy was to be implemented was due to eBay eliminating its own Standard Buyer Protection Plan in January for non-PayPal transactions, and it was meant to coincide with the improved PayPal Buyer Protection Plan. The change in buyer protection plans was announced by eBay Senior Vice President of Trust & Safety, Rob Chesnut on January 10, 2007.

eBay's Form 10-K Annual Report, filed with the United States Securities and Exchange Commission on February 28, 2007 stated that eBay had 222 million registered users as of December 31, 2006, yet it was recently reported that 23% (51,060,000) of those registered users have not accessed their accounts in a year or more. However, another source reported in January 2007 that only 79.8 million registered users are active, intimating that 142.2 million or 64% of the registered accounts are dormant.

This begs to ask the question why does eBay not temporarily disable the dormant accounts until members need to access them again? If eBay would temporarily disable dormant member accounts that have not been accessed for 30 days, eBay would be taking a step in the right direction, being proactive and protecting its members' accounts from being hacked by thieves. Yet eBay refuses to do this. How difficult can it be for eBay's IT Department, with its state-of-the-art technology to write a program to review the last access date of each account on its member database and then temporarily disable the accounts if access has not occurred in the last 30 days? Why would eBay prefer to waste unneedless customer service manpower hours manually taking down fraudulent listings and securing member accounts that were hacked? Why doesn't eBay want to minimize the inventory of dormant accounts potentially available to hackers? eBay has steadfastly denied that the server the member accounts are located on has been hacked, yet a well-known Romanian hacker by name of Vladuz has been able to hack eBay employee accounts and post messages on eBay message boards.

On January 8, 2007, eBay's Senior Vice President of Trust and Safety, Rob Chesnut announced the Launch of Safeguarding Member IDs (SMI). This new policy initiative is eBay's way of protecting its members from receiving fake Second Chance Offers. When bids on listings break the $200 threshold, eBay member IDs are disguised as Bidder1, Bidder2, Bidder3, etc. On the surface, this was a good idea, however, the transparency that eBay was so proud of on its platforms is now hidden; fake Second Chance Offers are as prevalent as ever and shill bidding has increased. eBay adamantly denies these accusations. Although not implemented as of yet, eBay is now strongly considering obscuring all bidders IDs at the opening bid.

With the implementation of SMI, it is now nearly impossible for bidders to check on their bidding competition. SMI is contrary to the third tenet of eBay's Community Values, the very foundation that eBay was built on:

eBay is a community that encourages open and honest communication among all its members. Our community is guided by five fundamental values:
We believe people are basically good.
We believe everyone has something to contribute.
We believe that an honest, open environment can bring out the best in people.
We recognize and respect everyone as a unique individual.
We encourage you to treat others the way you want to be treated.
In early March 2007, eBay removed the Marketplace Safety Tips message prominently displaced in the upper right hand corner of every listing for a shortened version of tips called Buy Safely. The longer list of tips has been condensed to two:

1. Check the seller's reputation - Read feedback comments
2. Check how you're protected
Gone from the listings is the warning message reminding members to never pay via instant money transfer services, such as Western Union and Moneygram.

To view eBay's detailed list of Marketplace Safety Tips click here.

At approximately the same time, eBay changed the color of the Place Bid button to make it more appealing and prominent within the listing, but removed the direct link to report excessive shipping charges. And, on the Bid Confirmation page, eBay again removed the warning message to never pay via instant money transfer services, such as Western Union and Moneygram. It was suggested that the warning message on the Bid Confirmation page was removed because members that unknowingly enter into off-eBay transactions never see the message, because they aren't placing bids.

It appears that eBay's priority is to hide fraud on its platforms. When fraudulent listings are reported to eBay, it usually takes the listings down and secures the hijacked accounts, but it also destroys any evidence that the fraudulent listings ever existed. Those that were duped have little evidence that the listing ever existed, and have little information to provide to either eBay or law enforcement. Can eBay state with a clear conscience that fraud doesn't exist on its platforms because it destroys the evidence that it ever existed?

eBay could put in a mechanism to temporarily disable all member accounts that have not been active for 30 days. eBay could revert back to bidder transparency and instead discontinue all Second Chance Offers. eBay could improve member education and require all new members to take tutorials and pass them before allowing them to bid or list on eBay; it should require all other members to take refresher tutorials annually. eBay could place selling limits on all new members and make them establish a buying and selling history before giving them free reign to list an abundant number of expensive items for sale on its platforms. eBay could remove all links from its email messages and instead send out email messages to its members to check their My eBay My Messages accounts for all messages, including invoices. eBay could send out a monthly email message to all members regarding fraud prevention, just like its competitor, Overstock.com does. eBay could put back the Marketplace Tips in its listings and revert back to the Bid Confirmation page it had previously with the warning message about not paying for transactions through instant money transfer services. eBay could include the category a listing is in at the top of the body of description in a large bold font so that its members could easily see it and determine if the item is in the correct category. eBay could treat all members equally and not overlook violations of some. eBay could be proactive and make a lot of positive changes if it really wanted to. Unfortunately, eBay does not want to implement any of these suggestions.

Therefore, since eBay does not want to take positive action to minimize the rampant fraud on its platforms, The Nekkid Truth is suggesting that if you have not accessed your eBay account in at least 30 days and if you do not have intentions to do so soon, that you begin the process to close your eBay account by clicking here. Do not allow your dormant account to become useable by hackers. We strongly advise you not to enter into any transactions on eBay until this arrogant Internet giant takes positive steps that are apparent to its members and it begins to implement additional safeguards to combat fraud.

However, if you must shop on eBay, we encourage you to take every precaution possible and familiarize yourself with the warning signs so that you do not become a victim of fraud. Do not take unnecessary risk. Pay for transactions only via PayPal and only with a credit card. For further information on how to protect yourself read the blog entries at The Nekkid Truth, review the threads on eBay's Trust & Safety message board, and take the eBay tutorials.

eBay needs to be held accountable for the fraud that proliferates on its platforms. Whether you are a victim of fraud on eBay or want eBay to have its venue status removed, write to the members of the House Subcommittee on Telecommunications and the Internet. Demand that this congressional subcommittee begin an investigation on eBay and ultimately have a hearing to review eBay's venue status.

If you are a victim of fraud on eBay and live in the United States or any of its commonwealth's or territories, also write to your state's, commonwealth's, or territory's Attorney General. A complete list of Attorneys General can be found by clicking here. From the National Association of Attorneys General website:

What does an Attorney General do?

As the chief legal officer of the states, commonwealths and territories of the United States, the Attorneys General serve as counselors to their legislatures and state agencies and also as the "People's Lawyer" for all citizens. Originating in the mid-13th century in the office of England's "King's Attorney," the office had become, by the American Revolution, one of advisor to the Crown and to government agencies.

In the United States, as the individual states and territories developed their own procedures, common law, constitution state government agencies and legislatures, and as representatives of the public interest. While varying from one jurisdiction to the next due to statutory and constitutional mandates, typical powers of the Attorneys General include the authority to issue formal opinions to state agencies; act as public advocates in areas such as child enforcement, consumer protections, antitrust and utility regulation; propose legislation; enforce federal and state environmental laws; represent the state and state agencies before the state and federal courts; handle criminal appeals and serious statewide criminal prosecutions; institute civil suits on behalf of the state; represent the public's interests in charitable trust and solicitations; and operate victim compensation programs.
Be proactive. Review the consumer protection alert bulletins on the Federal Trade Commission's website.

Don't allow eBay to continue to make its members the scapegoats for its own arrogance, ineptitude, short-sightedness and unwillingness to protect its members. Don't allow eBay to continue to blame its members for hijackings ... for clicking on links in spoof and phish email messages and on redirected links in listings on its platforms. Make eBay accountable.

David successfully slew Goliath.

Don't allow eBay to continue to be omnipotent. Take action, and make eBay impotent. There is no goodwill at eBay. Its public image and reputation are irrefutably tarnished.